ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


The healthcare sector runs on trust. Every record, every detail matters and that is why HIPAA was introduced. HIPAA, the Health Insurance Portability and Accountability Act, provides a structure to safeguard personal data, patients' confidential information and sensitive data. INTERCERT offers HIPAA compliance assessment services for your organization so that it stays aligned with regulations and protects what matters most and that is patient privacy.
HIPAA is a law set by U.S federal. Its main duty is to protect sensitive data of patients’ health. It is applicable to the industries that handle medical data, such as hospitals, clinics, insurers and vendors. This law sets a structure of rules for Protected Health Information (PHI) and how they are accessed, stored and shared.
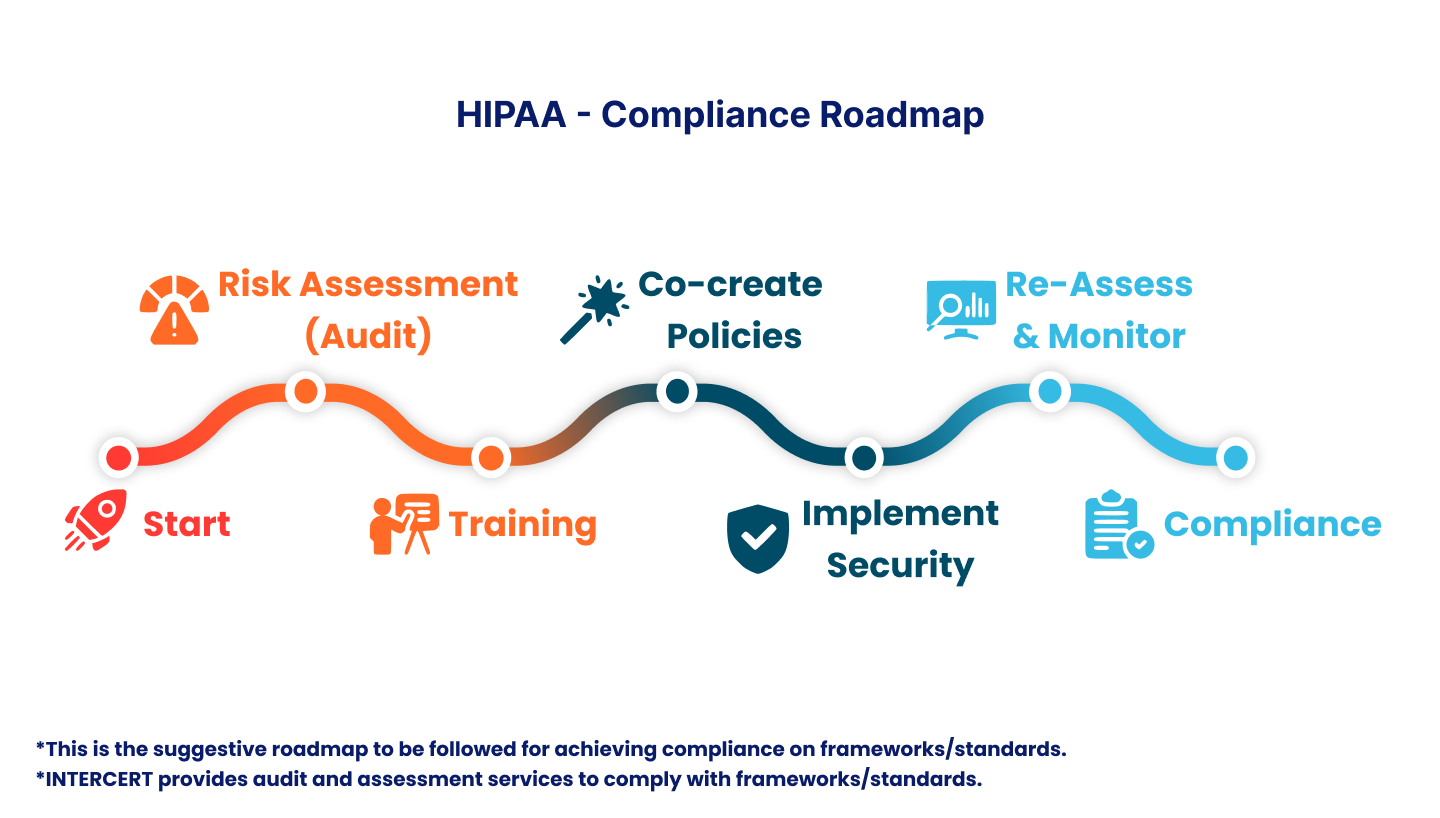
Here is a general overview of the key steps your organization should follow to achieve HIPAA compliance:

Conduct an initial assessment to determine whether the current process meets the requirements of standards or frameworks.
Identify the scope to understand inclusions and exclusions, which establishes boundaries, supports, goal achievement, and a clear path to achieving success.
Ensures a streamlined workflow, aligning processes to achieve goals while maintaining efficiency and quality.
Identify, develop, and implement solutions to meet requirements, improving and optimizing them to remain effective and aligned.
Provide training to boost skills, awareness, and understanding of handling tasks, managing risks, and applying the best methods to improve the process and requirements of the standard or framework requirements.
Conduct an audit to examine compliance with standards or framework requirements and provide an assessment report that includes compliance evaluation and improvement areas.
Ensure constant process improvement to enhance outcomes and drive efficiency and overall performance.
Understanding of Business Context
Confirmation of Audit Scope
Assignment of Auditor (CISA/CIPP/CIPM Certified)
Preparation of Audit Plan
Opening Meeting
Confirmation of Scope
Collection of Evidence
Closing Meeting
Preparation of Draft Report
Client approval on Draft Report
Delivery of final report attested by the CISA/CIPP/CIPM certified Auditor
Ensure sensitive health related data is safe from any breaches.
Build patient trust with strong privacy measures.
Ensures efficiency with streamlined data protection.
Enhanced trust and credibility by demonstrating commitment to patient privacy and data security.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com