ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


SOC 2 provides a security framework to protect sensitive data. If your organization have SOC 2 compliance you can manage cloud platforms, handle customer records or run digital services smoothly. This will build clients trust and transparency. SOC 2 ensures that your data is secure. INTERCERT offers SOC 2 assessments and attestation services to ensure your organization improve the system and achieve compliance standards.
SOC 2 is a framework set by the AICPA that covers critical areas such as security, availability, processing integrity, confidentiality and privacy. AICPA developed SOC 2 framework to assess service providers who handle financial data for others. It helps verify that you’re managing that responsibility with the right controls in place and you’re not just claiming to protect information but you’re doing it and proving it.
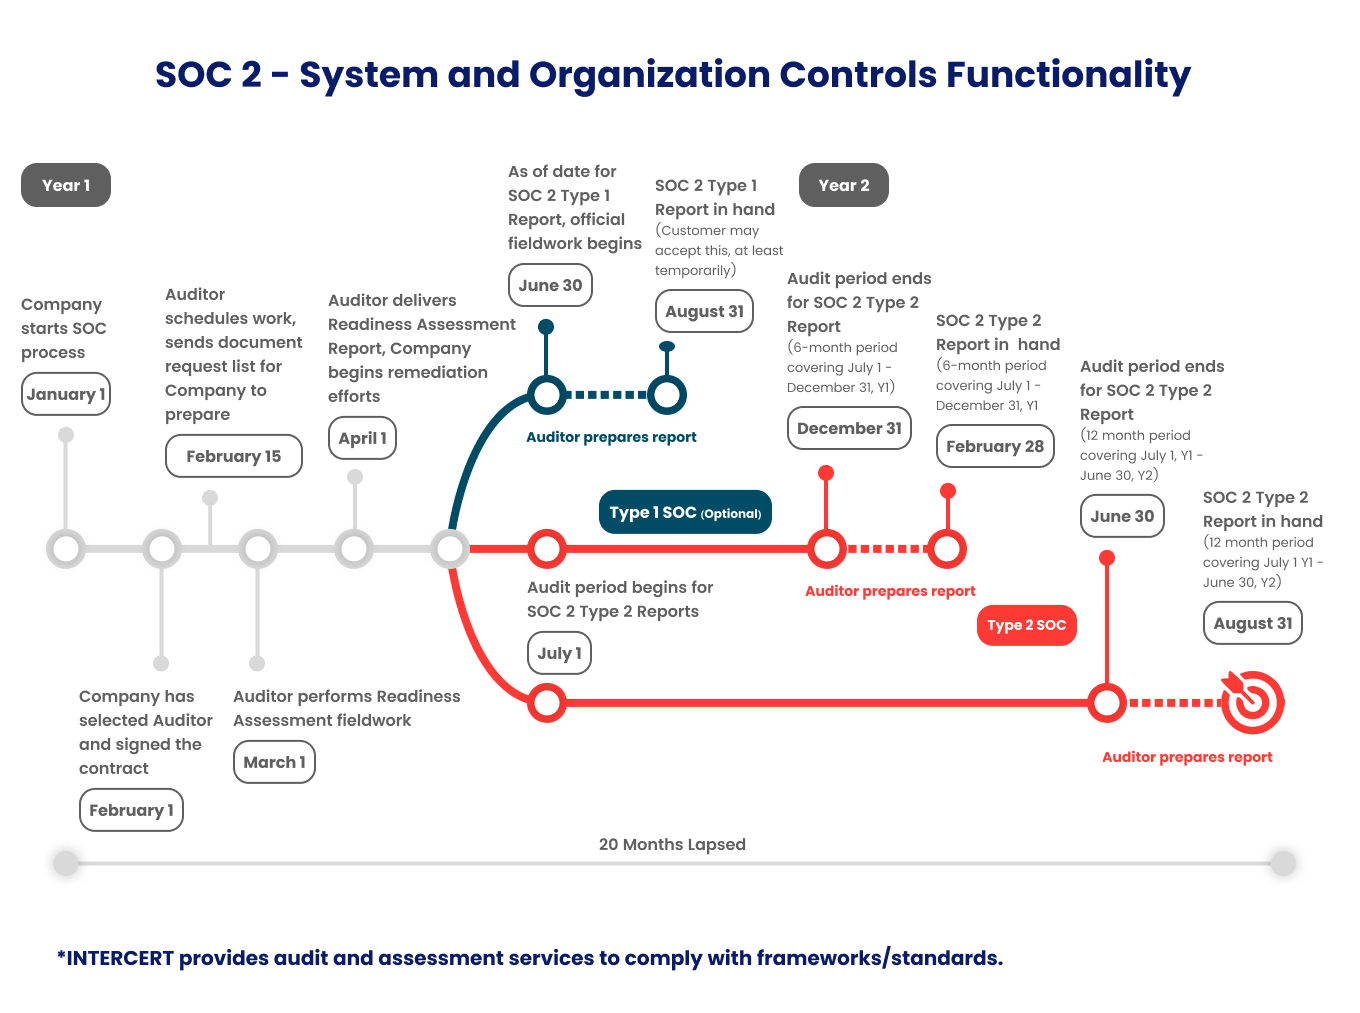
Here’s a general overview of the key steps involved in achieving SOC 2 compliance:

Conduct an initial assessment to determine whether the current process meets the requirements of standards or frameworks.
Identify the scope to understand inclusions and exclusions, which establishes boundaries, supports, goal achievement, and a clear path to achieving success.
Ensures a streamlined workflow, aligning processes to achieve goals while maintaining efficiency and quality.
Identify, develop, and implement solutions to meet requirements, improving and optimizing them to remain effective and aligned.
Provide training to boost skills, awareness, and understanding of handling tasks, managing risks, and applying the best methods to improve the process and requirements of the standard or framework requirements.
Conduct an audit to examine compliance with standards or framework requirements and provide an assessment report that includes compliance evaluation and improvement areas.
Ensure constant process improvement to enhance outcomes and drive efficiency and overall performance.
Understanding of Business Context
Confirmation of Audit Scope
Assignment of Auditor
Preparation of Audit Plan
Opening Meeting
Confirmation of Scope
Collection of Evidence
Testing of control implementation & Effectiveness
Closing Meeting
Preparation of Draft Report
Client approval on Draft Report
Delivery of SOC 2 Report Attested by the CPA (AICPA)
Ensures robust security postures to safeguard data.
Reduces the risk of data breaches with strong controls.
Enhances incident response to minimize downtime.
Strengthens data security to prevent cyber risks.
Commitment towards security, fostering trust and confidence among customers, partners, and investors.
Streamlines framework processes for easier regulatory compliance.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com