ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


The National Institute of Standards and Technology (NIST) Special Publication 800-53 provides comprehensive guidelines for securing federal information systems and organizations. INTERCERT offers NIST 800-53 compliance assessment services to help your organization implement information security controls and practices.
NIST Special Publication 800-53 provides a catalog of security controls and guidelines for federal information systems and organizations. It covers a wide range of security areas, including access control, incident response, risk assessment, and security assessment and authorization. NIST 800-53 is widely adopted by federal agencies and is also applicable to non-federal organizations seeking to enhance their cybersecurity posture.
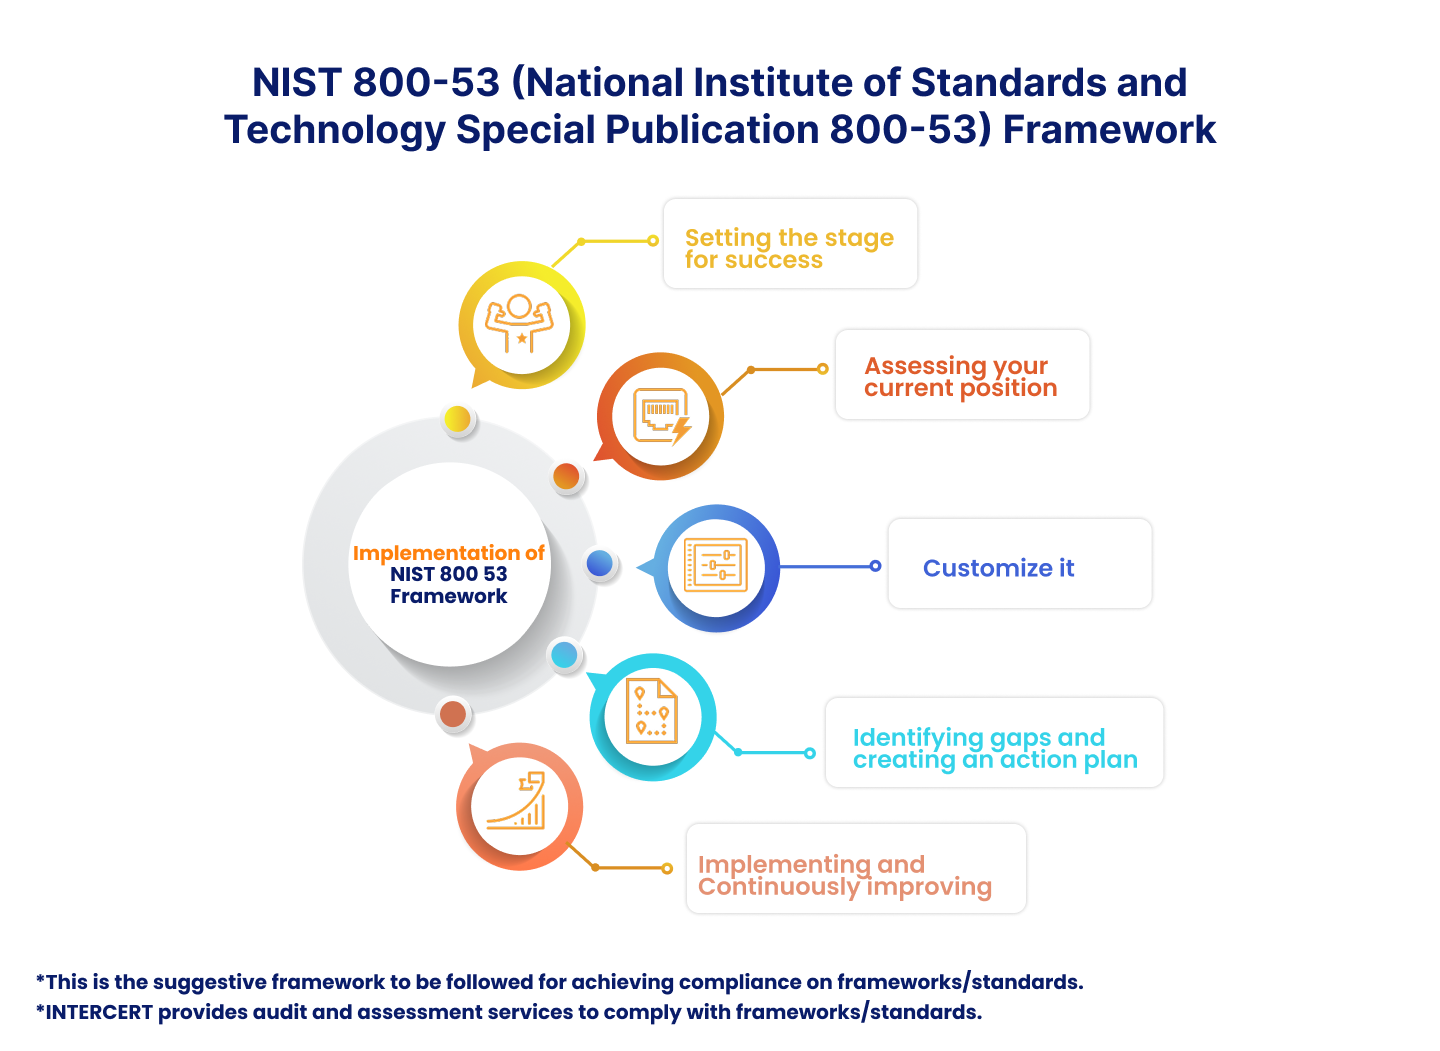
Here is a general overview of the key steps your organization should follow to achieve NIST 800-53 compliance:

Conduct an initial assessment to determine whether the current process meets the requirements of standards or frameworks.
Identify the scope to understand inclusions and exclusions, which establishes boundaries, supports, goal achievement, and a clear path to achieving success.
Ensures a streamlined workflow, aligning processes to achieve goals while maintaining efficiency and quality.
Identify, develop, and implement solutions to meet requirements, improving and optimizing them to remain effective and aligned.
Provide training to boost skills, awareness, and understanding of handling tasks, managing risks, and applying the best methods to improve the process and requirements of the standard or framework requirements.
Conduct an audit to examine compliance with standards or framework requirements and provide an assessment report that includes compliance evaluation and improvement areas.
Ensure constant process improvement to enhance outcomes and drive efficiency and overall performance.
Understanding of Business Context
Confirmation of Audit Scope
Assignment of Auditor (CISA Certified)
Preparation of Audit Plan
Opening Meeting
Confirmation of Scope
Collection of Evidence
Testing of control implementation & Effectiveness
Closing Meeting
Preparation of Draft Report
Client approval on Draft Report
Delivery of final report attested by the CISA certified Auditor
NIST SP 800-53 provides a catalog of security and privacy controls to help organizations build secure, resilient information systems. It provides you a roadmap to classify systems into three risk levels low, moderate or high risk and apply the right controls.
The framework centers on five areas:
1. Identify – Know assets and risks
2. Protect – Safeguard data
3. Detect – Monitor for threats
4. Respond – Act on incidents
5. Recover – Restore systems
In short, it’s a playbook of best practices that strengthens cybersecurity and keeps systems ready for evolving threats.
Strengthens security management within an organization with a trusted and standardized framework.
Establish trust with improved supply chain security.
Ensures security processes are streamlined with reduced operational cost.
Improves transparency with strong cybersecurity practices.
Easy to manage risk and compliance issues with reduced downtime.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com