ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


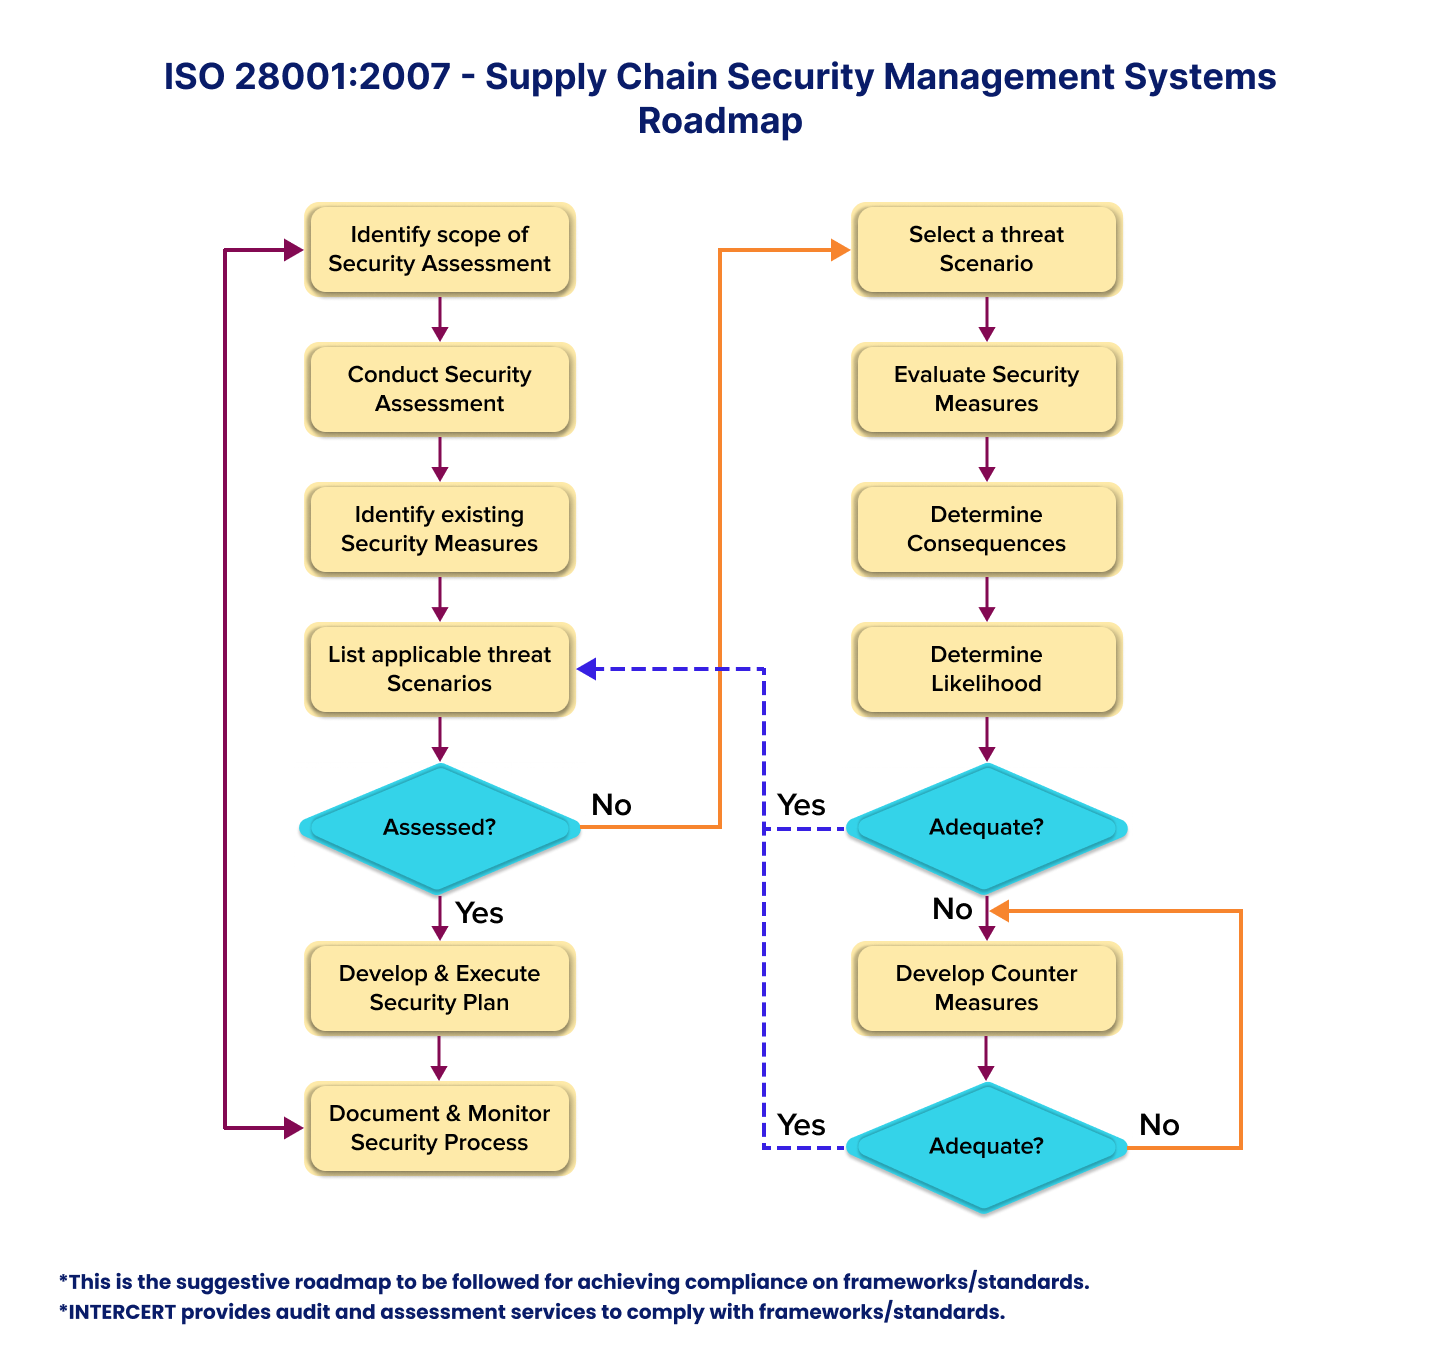
ISO 28001 is a global standard that provides a framework for organizations need to secure their supply chains. This standard sets a security management system that must be followed from manufacturing to distribution. The goal is simple that is to keep everything safe and moving without risk.
The standard provides a strong base for organizations to spot problems early and find risks and manage them to avoid issues like theft or unauthorized access. There is no jargon, no complexity, just a strong base to protect what matters across the supply chain.

Ensure a security strategy to identify risks and measure the impact. Risk assessments reveal the weak spots and vulnerabilities in the system to improve the overall security process.
Apply cybersecurity tools like firewalls and encryption to secure storage, surveillance and staff checks to build a control process. A clear emergency procedure needs to be set to combat natural disasters or attacks so that it matches the supply chain needs.
Regularly monitor the security controls and use audits, reporting and inspections to spot issues and improve the security process. Review any loopholes and threats to stay protected if a breach happens.
Establish a secure system in the supply chain to ensure suppliers, distributors and logistics follow the same policy to reduce weak points and build trust in the supply chain.
Enables customs authorities to build defenses and manage supply chain risks.
Ensures high-quality service and product reliability.
Includes cost-benefit analysis in risk assessments.
Prevents losses by improving inventory control.
Positions your business as a trusted supply chain partner.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com