ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


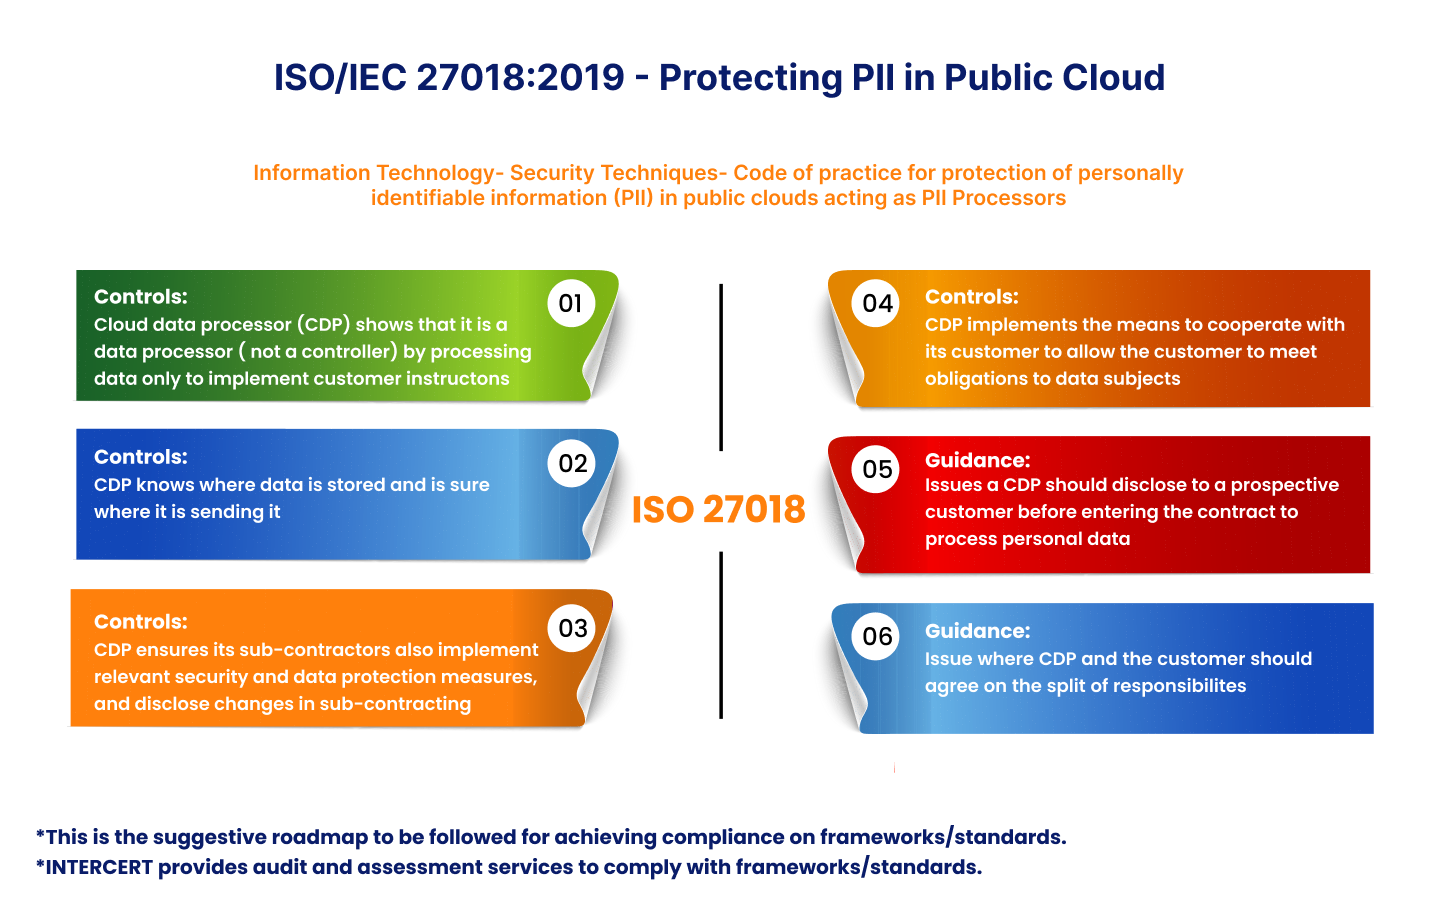
Cloud security is the most important area of data protection in a digital world. With ISO/IEC 27018 organizations can secure personal data in the cloud. This standard is built for cloud privacy. It provides a structured framework for how cloud service providers should manage Personally Identifiable Information (PII). It manages key problems around data privacy and ensures that PII stored or processed in the cloud is handled with the highest level of security and care.

Cloud providers should never manage personal data without consent. Consent simply means you have to give permission. You should also be informed about how your data is used, stored or shared.
This ensures that you know what the cloud provider collect, manage and uses your personal data for. You will have to understand how your personal data in the cloud is being collected, processed & secured.
This principle focuses on the application of robust security controls including strong safeguards such as encryption and strong access control measures, on the storing of your data.
Cloud providers must notify you and the relevant authorities without delay so that appropriate action can be taken to limit the possibility of harm.
Cloud service providers must develop clear procedures regarding the management of your personal data and provide assurance of compliance.
Ensures that your personal data is secure in cloud environments.
Strengthens cloud security while building customer trust.
Builds strong and trusted relationships with clients.
Ensures there are no compliance risks to avoid financial penalties.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com