ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


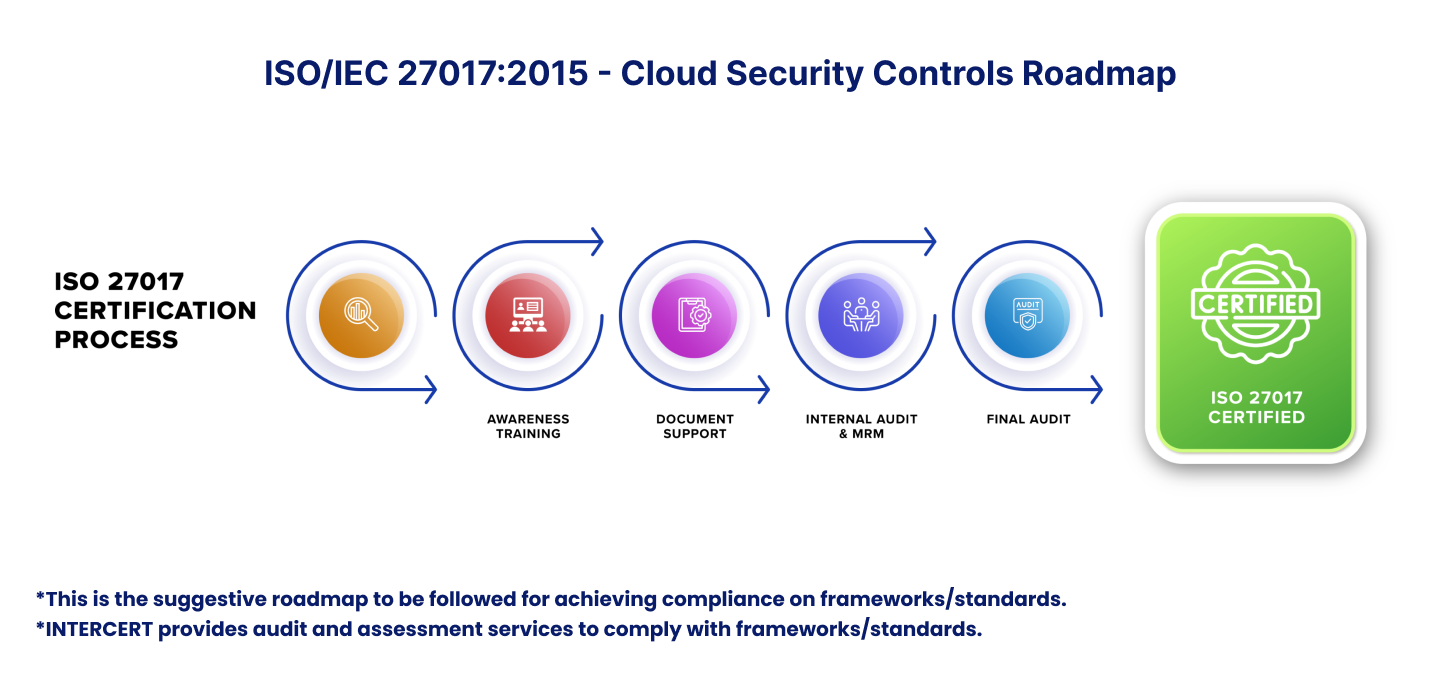
ISO/IEC 27017 is a global standard built for cloud security. It provides a structured framework to put the right security controls when using cloud services. This standard is an extension of ISO 27001 but focuses only on the cloud security.
It improves the system to identify common risks that come with storing data and running systems in the cloud. From handling shared responsibilities to managing access it helps organizations stay secure in a cloud-first world.

This standard provides a structure to setup cloud security and make necessary frameworks to manage key areas like data privacy, service availability and following the law.
ISO/IEC 27017 defines the roles and responsibilities of cloud service providers (CSPs) and cloud service customers (CSCs) clearly. This standard clearly defines the security responsibilities which makes the whole process transparent.
Managing security in the cloud is an fast and ongoing process. This principle focuses on putting strong, consistent processes in place to handle risks, respond to incidents and meet legal or regulatory needs.
To secure cloud-based information.
Supports business growth through reliable cloud security.
Reducing security risks and preventing data breaches.
Protects against legal fines and compliance failures to strengthen reputation.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com