ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


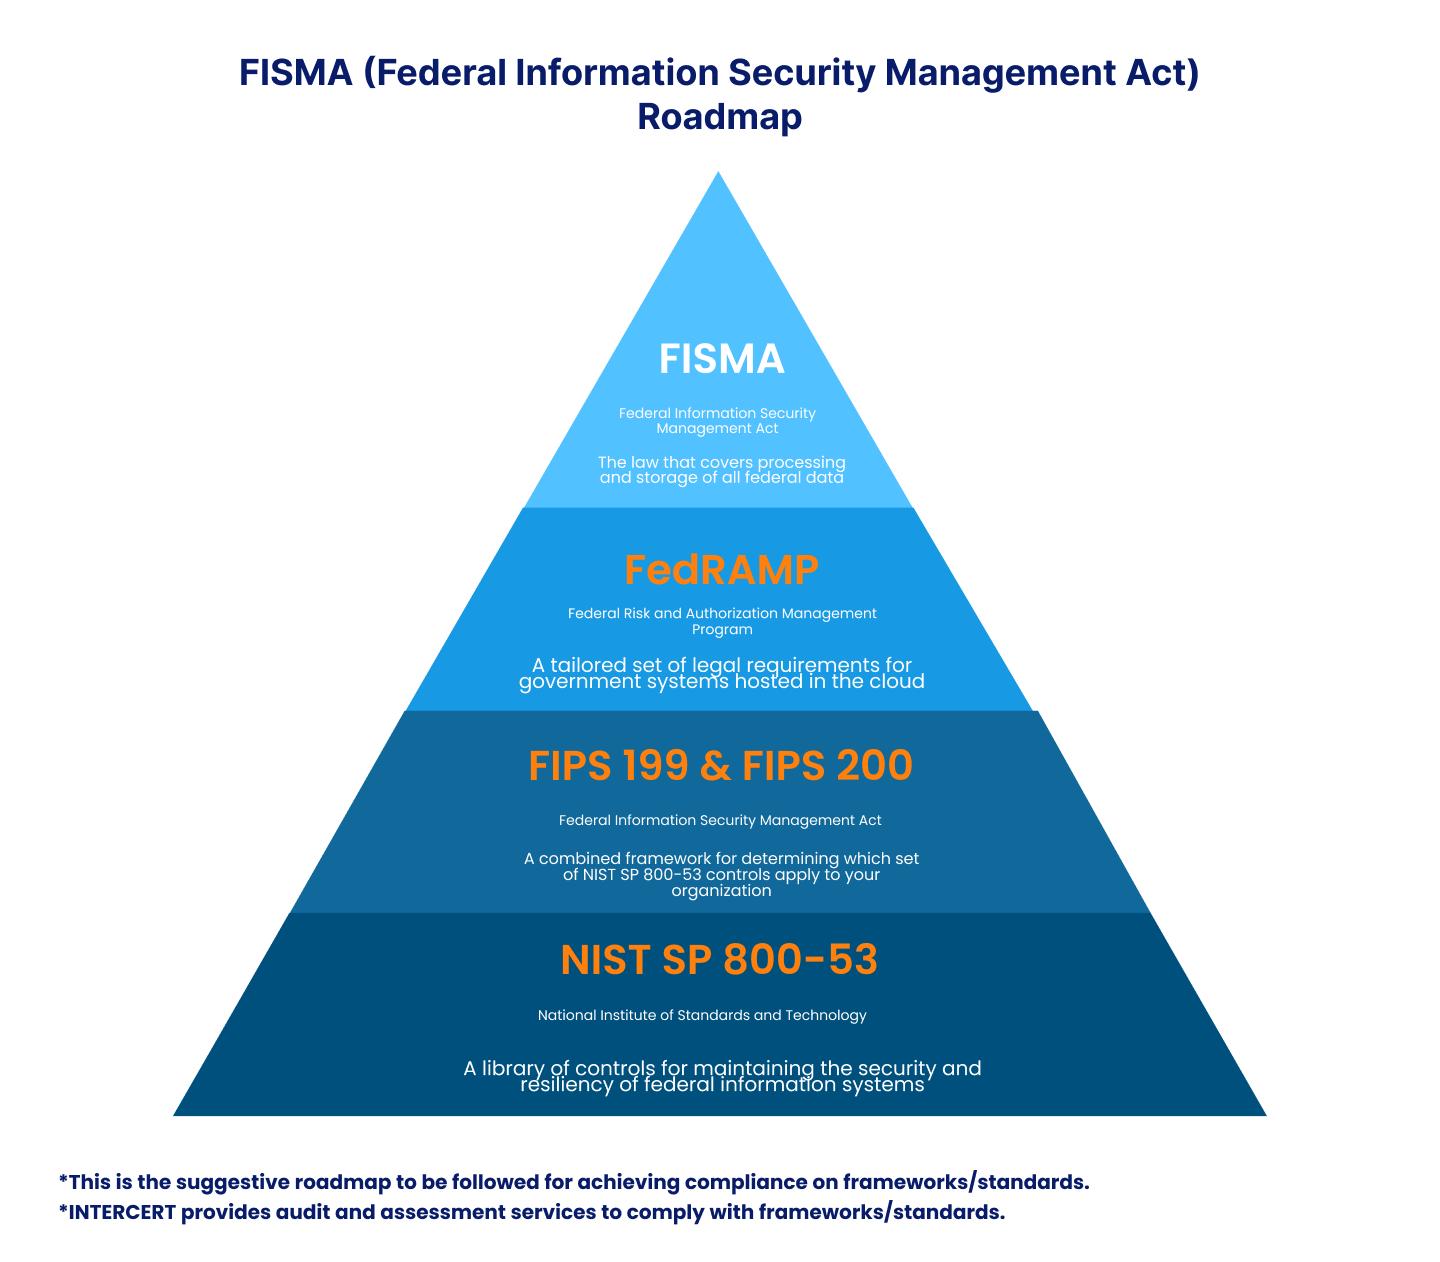
The Federal Information Security Management Act (FISMA) is developed to establish a structured framework to protect federal information and information systems. It sets guidelines to protect the federal information systems against threats and risks. INTERCERT offers FISMA compliance assessment services to meet these strict requirements and enhance your information security posture.
FISMA is a United States federal law enacted in 2002 that mandates federal agencies to develop, document and implement an information security program to protect their information and information systems. FISMA outlines specific requirements for managing information security risks, ensuring the confidentiality, integrity and availability of federal information.
Here is a general overview of the key steps your organization should follow to achieve FISMA compliance:

Conduct an initial assessment to determine whether the current process meets the requirements of standards or frameworks.
Identify the scope to understand inclusions and exclusions, which establishes boundaries, supports, goal achievement, and a clear path to achieving success.
Ensures a streamlined workflow, aligning processes to achieve goals while maintaining efficiency and quality.
Identify, develop, and implement solutions to meet requirements, improving and optimizing them to remain effective and aligned.
Provide training to boost skills, awareness, and understanding of handling tasks, managing risks, and applying the best methods to improve the process and requirements of the standard or framework requirements.
Conduct an audit to examine compliance with standards or framework requirements and provide an assessment report that includes compliance evaluation and improvement areas.
Ensure constant process improvement to enhance outcomes and drive efficiency and overall performance.
Understanding of Business Context
Confirmation of Audit Scope
Assignment of Auditor (CISA Certified)
Preparation of Audit Plan
Opening Meeting
Confirmation of Scope
Collection of Evidence
Closing Meeting
Preparation of Draft Report
Client approval on Draft Report
Delivery of final report attested by the CISA certified Auditor
Enhances cybersecurity by providing control over systems and data.
Early risk detection saves them before they turn into real problems.
Keeps sensitive information safe from leaks and insider threats.
Builds trust by protecting personal and confidential data from misuse.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com