ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


The world is interconnected and so is their network and information system. Securing these system is critical for resilience and reliability of essential services and digital infrastructure. EU NIS 2 stands for European Union Network and Information Security Directive that measures a high common level of cybersecurity across European Union. INTERCERT offers NIS2 compliance assessment services to enable your organization and ensure they meet these requirements to enhance their cybersecurity system.
The Network and Information Security Directive (NIS2) is an updated version of the original NIS Directive, aimed at improving the cybersecurity of networks and information systems within the European Union. NIS2 introduces stricter security requirements, a broader scope of application and enhanced incident reporting obligations for essential and important entities operating in various sectors, including energy, transport, banking, health and digital infrastructure.
Here is a general overview of the key steps your organization should follow to achieve EU NIS2 compliance:

Conduct an initial assessment to determine whether the current process meets the requirements of standards or frameworks.
Identify the scope to understand inclusions and exclusions, which establishes boundaries, supports, goal achievement, and a clear path to achieving success.
Ensures a streamlined workflow, aligning processes to achieve goals while maintaining efficiency and quality.
Identify, develop, and implement solutions to meet requirements, improving and optimizing them to remain effective and aligned.
Provide training to boost skills, awareness, and understanding of handling tasks, managing risks, and applying the best methods to improve the process and requirements of the standard or framework requirements.
Conduct an audit to examine compliance with standards or framework requirements and provide an assessment report that includes compliance evaluation and improvement areas.
Ensure constant process improvement to enhance outcomes and drive efficiency and overall performance.
Understanding of Business Context
Confirmation of Audit Scope
Assignment of Auditor (CISA Certified)
Preparation of Audit Plan
Opening Meeting
Confirmation of Scope
Collection of Evidence
Testing of control implementation & Effectiveness
Closing Meeting
Preparation of Draft Report
Client approval on Draft Report
Delivery of final report attested by the CISA certified Auditor
The EU’s NIS2 Directive strengthens cybersecurity rules for essential and important entities across sectors like energy, transport, healthcare, digital services and more. To comply, organizations must focus on:
Have clear policies to identify and reduce cyber risks, including risks from your suppliers and partners.
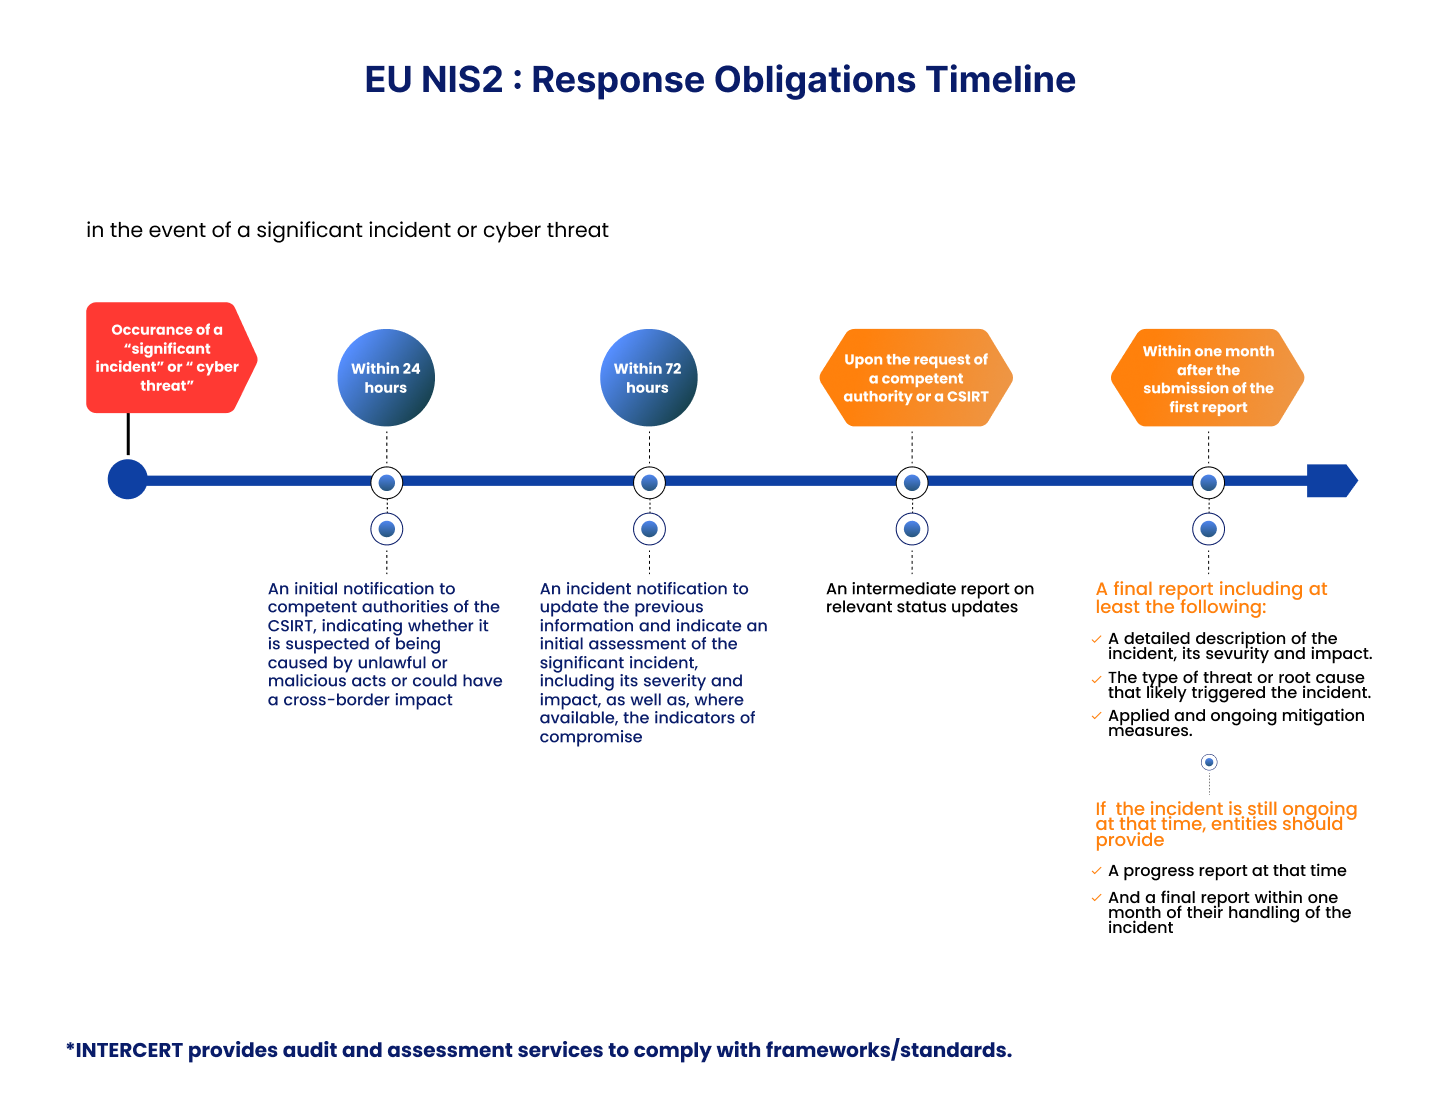
Report major cyber incidents fast: notify within 24 hours, give details within 72 hours and send a final report within a month.
Put core safeguards in place - encryption, access controls, patching, monitoring, backups and supply chain security.
Executives must oversee compliance and can be held personally liable if security measures are ignored.
Ensure operations can keep running during cyberattacks. Have recovery plans tested and ready.
Work with national authorities and share threat intelligence when required to strengthen collective defense.
Understand that non-compliance can mean heavy fines, legal consequences for leaders, and reputational harm.
Ensures data breaches, malware and unauthorized access are protected.
Enhances security measures against cyber threats with no downtime and fast responses.
Establishes trust and transparency among clients and investors with compliance.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com