ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


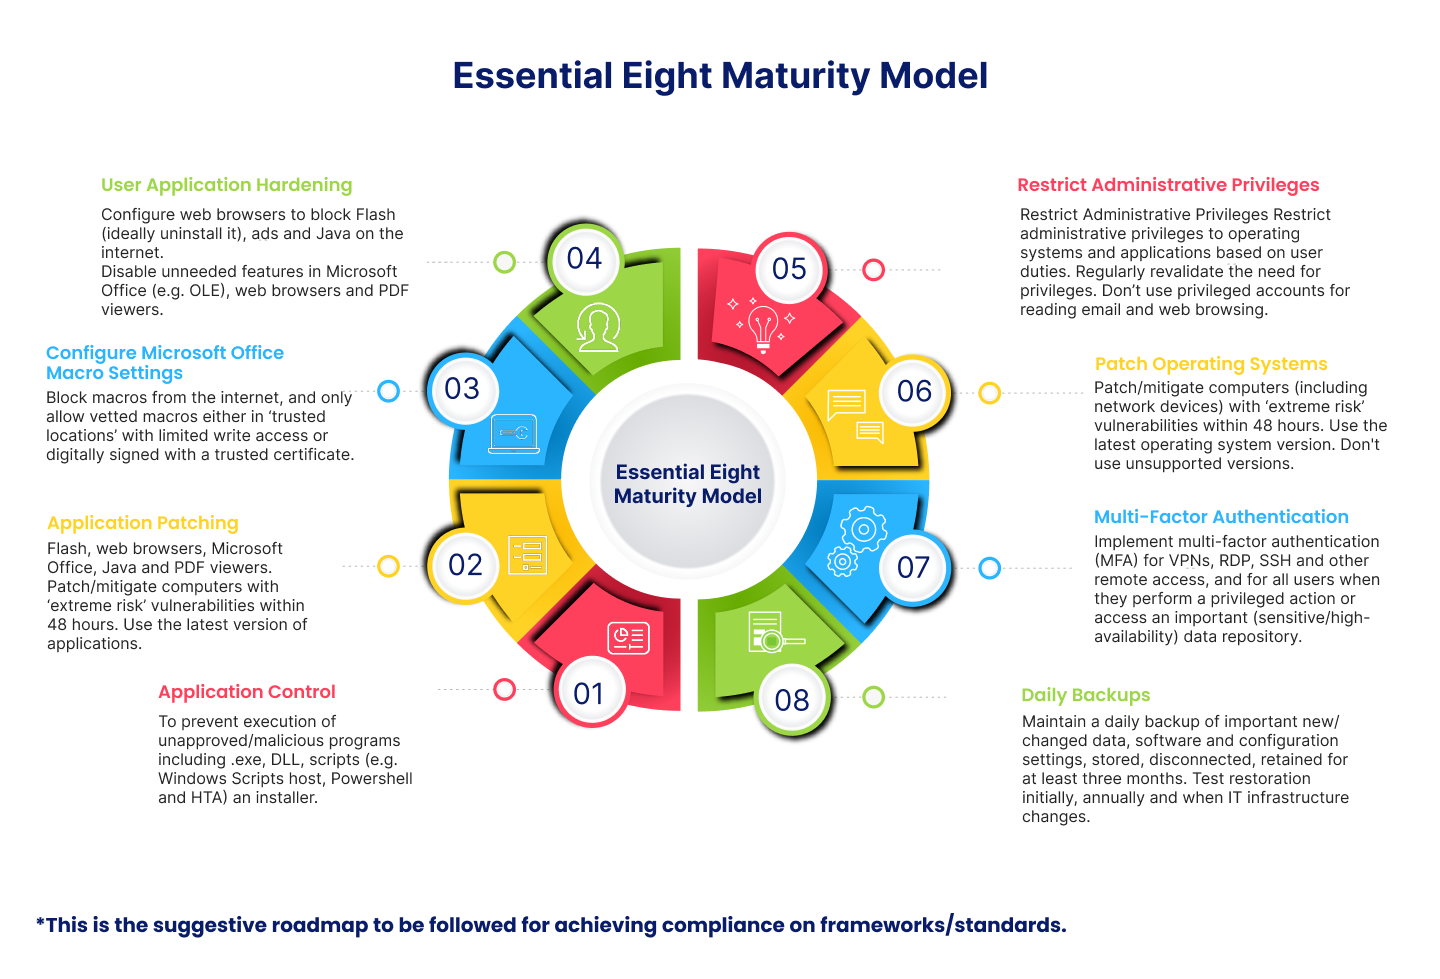
Cyber threats are evolving and it is the responsibility of the organization to develop a security measure to protect digital assets of organization. The Essential Eight Maturity Model is developed by the Australian Cyber Security Centre (ACSC). This standard is developed to help organizations manage cyber risks. INTERCERT offers Essential Eight compliance assessment services to adopt these best practices and enhance cybersecurity.
The Essential Eight Maturity Model is a framework that outlines eight essential strategies to mitigate cyber risks. Each model consists of three levels of maturity to guide organizations in implementing and refining these strategies. The Essential Eight covers a broad range of security practices, from application whitelisting and patch management to user application hardening and daily backups.
Here is a general overview of the key steps your organization should follow to achieve this compliance:

Conduct an initial assessment to determine whether the current process meets the requirements of standards or frameworks.
Identify the scope to understand inclusions and exclusions, which establishes boundaries, supports, goal achievement, and a clear path to achieving success.
Ensures a streamlined workflow, aligning processes to achieve goals while maintaining efficiency and quality.
Identify, develop, and implement solutions to meet requirements, improving and optimizing them to remain effective and aligned.
Provide training to boost skills, awareness, and understanding of handling tasks, managing risks, and applying the best methods to improve the process and requirements of the standard or framework requirements.
Conduct an audit to examine compliance with standards or framework requirements and provide an assessment report that includes compliance evaluation and improvement areas.
Ensure constant process improvement to enhance outcomes and drive efficiency and overall performance.
Understanding of Business Context
Confirmation of Audit Scope
Assignment of Auditor (Technical ICT Qualified Auditor)
Preparation of Audit Plan
Opening Meeting
Confirmation of Scope
Collection of Evidence
Testing of control implementation & Effectiveness
Closing Meeting
Preparation of Draft Report
Client approval on Draft Report
Delivery of attested final report by certified technical ICT qualified Auditor
Reduces the chance of cyber threats.
Implementing these strategies helps boost your overall cyber security.
Lower security risks lead to fewer financial setbacks.
It gives organizations a trusted framework to meet audit requirements.
The strategies minimize gaps that lead to data compromise.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com