ISO/IEC 27001:2022 Information Security Management Systems
Information Security Management Systems


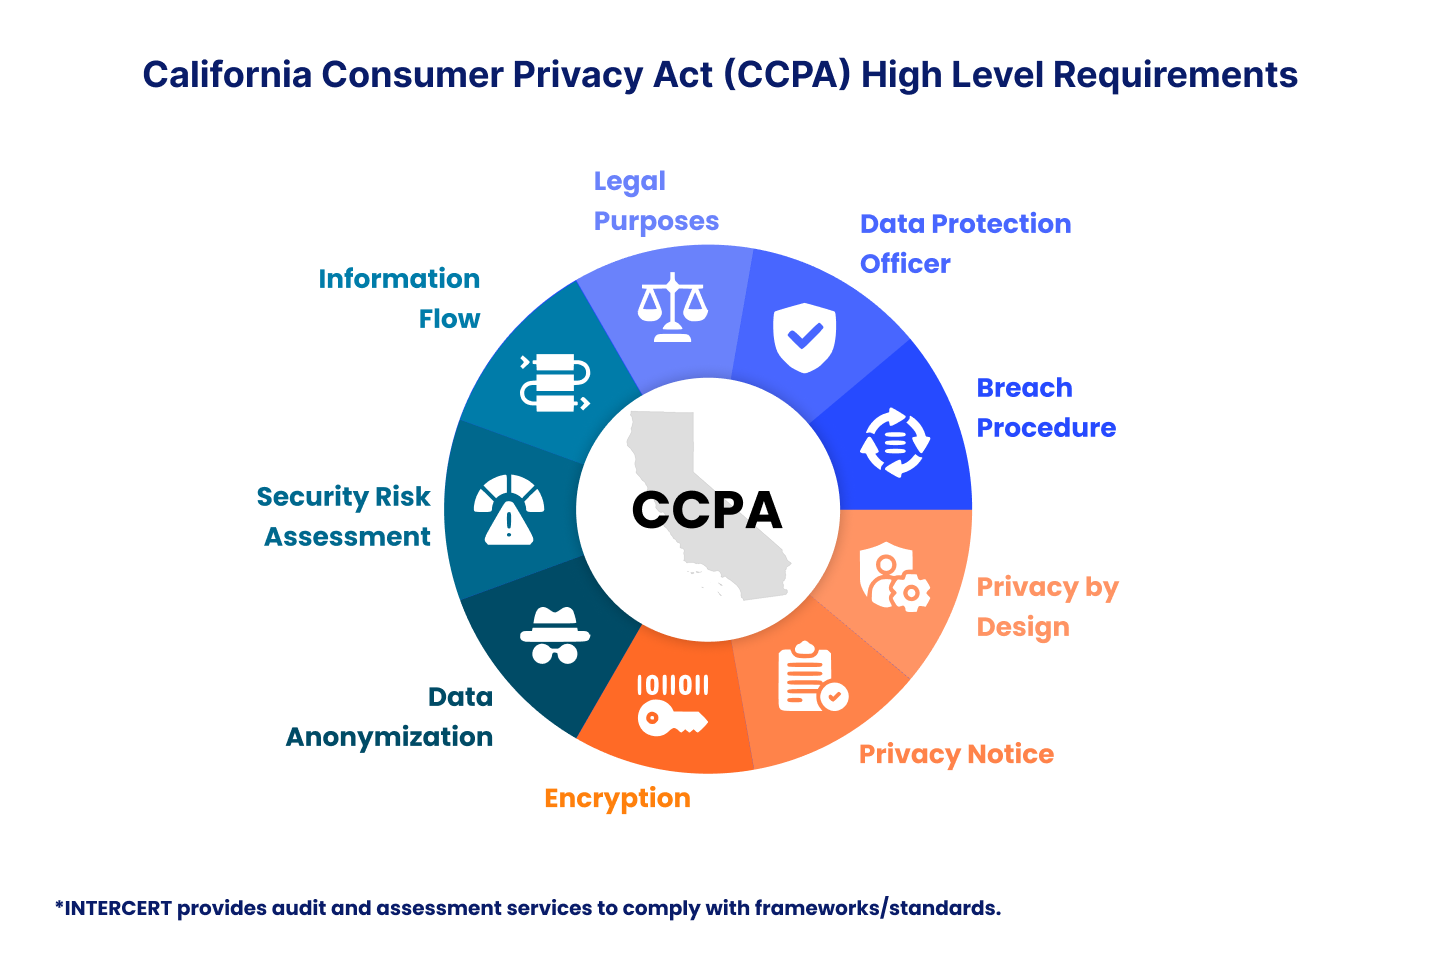
Consumers expect control over their personal data and expects data privacy. The California Consumer Privacy Act (CCPA) provides a framework for businesses and suggests how they collect, use and disclose customers' personal information. It gives the customers complete right to know what data is collected, how it’s used and who it’s shared with. Organizations must comply with CCPA to ensure transparency and accountability in handling personal information. INTERCERT offers compliance assessments to ensure your data practices align with the law.
The California Consumer Privacy Act (CCPA) is a data privacy law that grants California residents control over their personal information. It allows customers and clients to know what data is collected, shared or sold and to request its deletion if needed. The law applies to businesses that meet certain criteria and operate with personal data of California consumers.
Here is a general overview of the key steps your organization should follow to achieve CCPA compliance:

Conduct an initial assessment to determine whether the current process meets the requirements of standards or frameworks.
Identify the scope to understand inclusions and exclusions, which establishes boundaries, supports, goal achievement, and a clear path to achieving success.
Ensures a streamlined workflow, aligning processes to achieve goals while maintaining efficiency and quality.
Identify, develop, and implement solutions to meet requirements, improving and optimizing them to remain effective and aligned.
Provide training to boost skills, awareness, and understanding of handling tasks, managing risks, and applying the best methods to improve the process and requirements of the standard or framework requirements.
Conduct an audit to examine compliance with standards or framework requirements and provide an assessment report that includes compliance evaluation and improvement areas.
Ensure constant process improvement to enhance outcomes and drive efficiency and overall performance.
Understanding of Business Context
Confirmation of Audit Scope
Assignment of Auditor (CISA/CIPP/CIPM Certified)
Preparation of Audit Plan
Opening Meeting
Confirmation of Scope
Collection of Evidence
Closing Meeting
Preparation of Draft Report
Client approval on Draft Report
Delivery of final report attested by the CISA/CIPP/CIPM certified Auditor
Protects consumer data with strong privacy measures.
Strengthens company reputation with compliance.
Helps businesses attract privacy-conscious consumers.
Ensures ethical and reliable data collection.
Reduces risks of fines and non-compliance issues.
Establishes data security posture to improve privacy.


 2001 Timberloch Place - Suite 500, The Woodlands, Texas 77380, United States
©2026 Intercert. All Rights Reserved
 +1 (281) 720-3261
 info@intercert.com